Week three: WordPress almost caught up with .env

By · 2 November 2026 · 5 min read

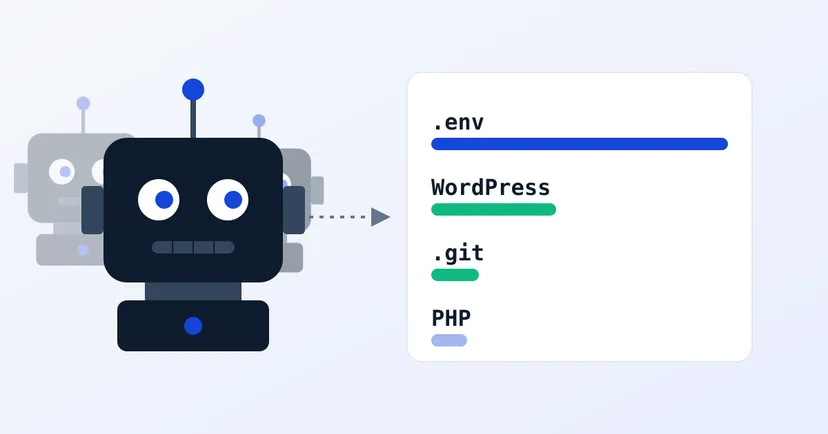
Illustration of a bot with a bar chart for week three: .env and WordPress almost the same length, followed by PHP and .git

Last week we wrote about the second week of the sensor on digimasi.com: more bots, and WordPress requests doubled. Now the third week is complete, from Monday 26 October to Sunday 1 November. This time it was not just more bots. The number of requests jumped too, and WordPress almost caught up with .env at the top.

The numbers

  • 2,976 requests from 179 IP addresses, recorded from 26 October at 00:00 Jakarta time (UTC+7) to the end of 1 November.
  • Those addresses are registered in 29 countries. That is where the servers are, not necessarily where the people are.
  • One network sent about a third of all requests: 1,000 requests from 22 addresses.
  • 9 requests carried a guessed username or password, sent to login pages that do not exist.

None of them succeeded. The files they asked for simply do not exist on our website, so every one of them got a "not found" page.

Compared with the second week

  • Requests up by about two thirds: from 1,809 to 2,976. IP addresses rose from 137 to 179. Each address sent about 17 requests on average, up from about 13. So this week the bots were both more numerous and busier.
  • WordPress rose again, more than doubling: from 395 to 936 requests, and from 72 to 100 addresses. It is now almost level with .env (986).
  • .env is still number one, but barely grew: from 936 to 986 requests. Its share fell from about half to a third. The number of addresses looking for it still grew, from 50 to 66.
  • PHP files almost tripled: from 112 to 313 requests. /index.php alone was requested 54 times, but from only 5 addresses.
  • The .git folder rose again: from 150 to 253 requests, and from 42 to 63 addresses. /.git/config is still the second most requested path (83 times, from 50 addresses).

What they looked for

  • Secret .env configuration files (986 requests, 66 addresses). Seven of the ten most requested paths are variations of .env: /.env (89), /.env.local (51), /.env.backup (47), /.env.bak (45), /.env.production (41), /.env.save (38) and /.env.old (35).
  • WordPress (936 requests, 100 addresses). More than half of all addresses that came this week tried WordPress. Our website does not use WordPress.
  • PHP files (313 requests, 36 addresses). Our website does not use PHP either.
  • The .git code history folder (253 requests, 63 addresses).
  • Other configuration files (221 requests, 40 addresses).
  • Cloud and server keys (96 requests, 31 addresses). For the first time, /.aws/credentials entered the top ten (35 requests from 24 addresses). That file holds the access keys to an Amazon Web Services account.
  • Backup files (72 requests, 7 addresses).
  • Admin panels (56 requests) and framework-specific paths (43 requests). The latter rose from a single request last week.

Worth noting: one network keeps growing

The second week felt more spread out. This week one network stood out again: TECHOFF SRV LIMITED sent 1,000 requests from 22 addresses, about a third of the total. Over three weeks it has kept climbing: 56 requests in the first week, 273 in the second and 1,000 this week. Google LLC stayed steady (628 requests from 30 addresses), followed by TC DATACENTER (320 from 10 addresses), DigitalOcean (221 from 37 addresses) and Cloudflare (140 from 14 addresses). One address at LIGHT NODE LIMITED sent 60 requests on its own. The network name is the owner of the address block, usually a server or cloud provider. Anyone who rents a server there can use it, so it does not mean the company itself sent the requests.

The countries shifted as well. The Netherlands is now far ahead (1,100 requests from 32 addresses), followed by the United States (399), Poland (327), France (206) and Singapore (151). Germany, which sent 950 requests in the first week, sent only 104 this week. Brazil and Thailand entered the top ten for the first time.

About the login guesses

There were 9 login guesses, down from 16 last week. All of them went to login pages that do not exist on our website. As in the two weeks before, none of them used a stock username such as "admin", so the username list in the weekly record is empty again.

Check your own website

You can check all of this yourself in five minutes, on your own website:

  • Open yourdomain.com/.env in a browser. You should see "not found". If you see the file's contents instead, move the file out of the public folder right away, then change every password and key in it.
  • Try the variations too: /.env.local, /.env.backup, /.env.bak, /.env.production. Bots guess these names every day.
  • Open yourdomain.com/.git/config. That should also say "not found". If you see text, your .git folder can be opened by anyone, and your website's code history with it.
  • Open yourdomain.com/.aws/credentials. If that file opens, anyone can use your cloud account. Remove it from the website folder, then disable the key in your AWS account and create a new one.
  • If you use WordPress: turn off xmlrpc.php if you do not need it, limit login attempts, keep plugins updated and turn on two-step verification for admin accounts. This week 100 different addresses tried WordPress on our website, and we do not use WordPress at all.

About this data

We only observe. All the data comes from bots that came to digimasi.com on their own; we never scan other people's websites, and we do not show IP addresses here. Addresses that clearly attacked us are reported to AbuseIPDB. The full method is on the methodology page, and each week's numbers are on the weekly record page.

Data: Digimasi security research, weekly sensor records (https://doi.org/10.5281/zenodo.23655270).

We will keep recording and comparing the results week by week.